Git for Specific Industries: Tailored Version Control Use Cases
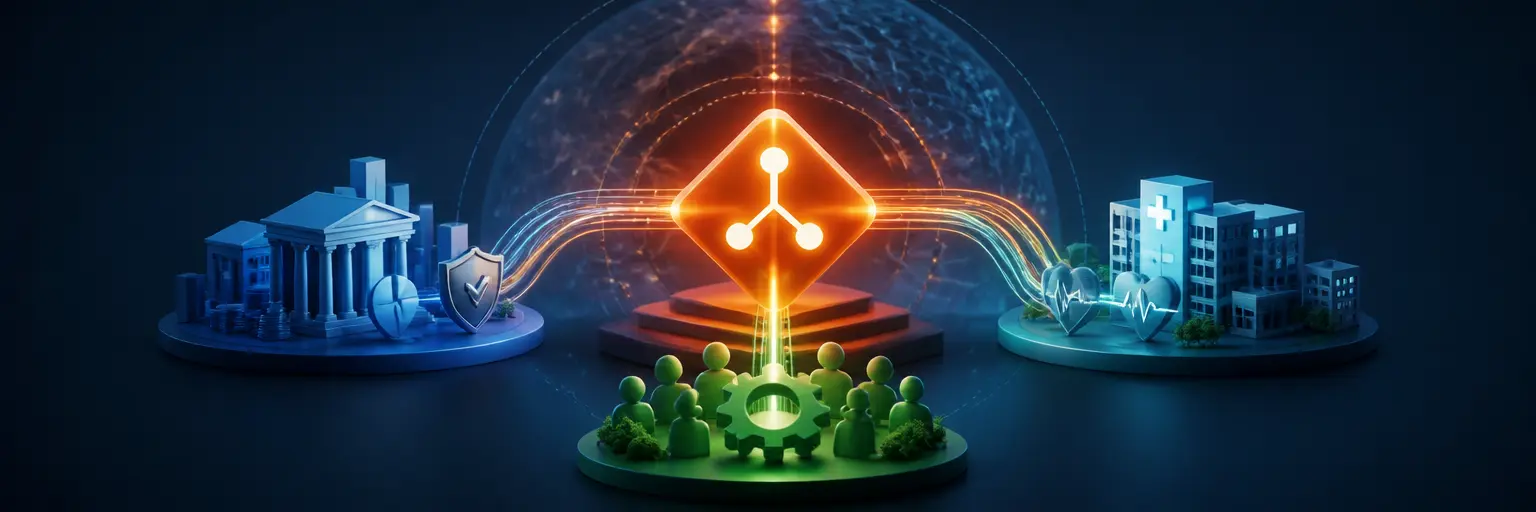
Explore how Git and version control support the specialized requirements of finance, healthcare, open source, and other regulated or collaborative industries. This guide explains practical workflows, compliance strategies, security controls, and Git-based automation for teams building reliable software in complex environments.
💰 Git Workflows for Finance and FinTech
Financial institutions and FinTech teams use Git to manage banking applications, payment platforms, trading systems, and data services with greater consistency. Readers can expect guidance on protected branches, peer review, audit-ready commits, and controlled releases. Git workflows can separate experimental development from production code while supporting CI/CD pipelines that test security, performance, and regulatory requirements before deployment.
🏥 Git in Healthcare and Medical Software
Healthcare software requires careful handling of patient data, clinical workflows, and safety-critical changes. This subcategory explores how Git supports electronic health record integrations, medical devices, telehealth platforms, and health analytics without placing sensitive information in repositories. Learn about access control, secret management, traceable changes, reproducible builds, and documented approvals that help development teams align version control with privacy and compliance responsibilities.
🌍 Git for Open Source Projects
Open source communities depend on Git for distributed collaboration across countries, time zones, and experience levels. Expect practical advice on forks, pull requests, issue tracking, semantic versioning, release tags, and contributor guidelines. These practices make it easier to review code, welcome new contributors, resolve merge conflicts, and maintain project quality while preserving transparent development histories.
🔐 Security, Compliance, and Industry Governance
Industry-specific Git usage often requires more than basic branching and merging. Learn how organizations can combine GitHub, GitLab, or self-hosted Git servers with least-privilege permissions, signed commits, vulnerability scanning, dependency management, and audit logs. Effective governance also includes repository policies, automated checks, secure secrets handling, retention rules, and documented approval workflows for high-risk changes.
⚙️ CI/CD and Specialized Delivery Pipelines
Git becomes especially valuable when connected to automated testing and deployment systems. This section explains how teams can build industry-focused CI/CD pipelines for compliance checks, infrastructure validation, container security, and staged releases. Readers will discover how branch strategies, environment protection, automated rollback, and continuous monitoring help deliver software safely while reducing manual errors and improving development velocity.
Frequently Asked Questions
How is Git used differently in finance and healthcare?
Both industries use Git for collaboration, traceability, testing, and controlled releases, but their controls may differ. Financial teams often emphasize transaction integrity, audit evidence, and risk management. Healthcare teams additionally prioritize privacy, patient safety, and protection of regulated health information. In both cases, repositories should exclude secrets and sensitive production data.
Can Git help organizations meet compliance requirements?
Git can support compliance by recording who changed code, what changed, when it changed, and how the change was reviewed. However, Git alone does not guarantee compliance. Teams should combine repository history with access controls, signed commits, approval policies, automated security checks, audit logging, and formal processes appropriate to their industry.
What Git branching strategy works best for regulated industries?
There is no universal strategy, but many regulated teams use protected main branches, short-lived feature branches, mandatory reviews, and release branches for approved versions. The best approach depends on deployment frequency, risk, team size, and audit needs. Automated tests and status checks should prevent unreviewed or failing code from reaching production.
How do open source projects manage Git contributions?
Most open source projects use public repositories, forks, pull requests, issue templates, and automated checks. Maintainers define contribution guidelines, coding standards, review expectations, and licensing rules. Continuous integration can test every proposed change, while release tags and changelogs help users identify stable, supported versions of the software.
Should sensitive industry data be stored in a Git repository?
No. Patient records, financial credentials, encryption keys, private tokens, and confidential customer data should not be committed to Git. Use secure secret managers, encrypted configuration services, and carefully designed access controls instead. If sensitive information is committed accidentally, remove it from history, rotate exposed credentials, and investigate the incident promptly.